/ Services / 01
Threat Detection and Response
Included in every plan
What this covers
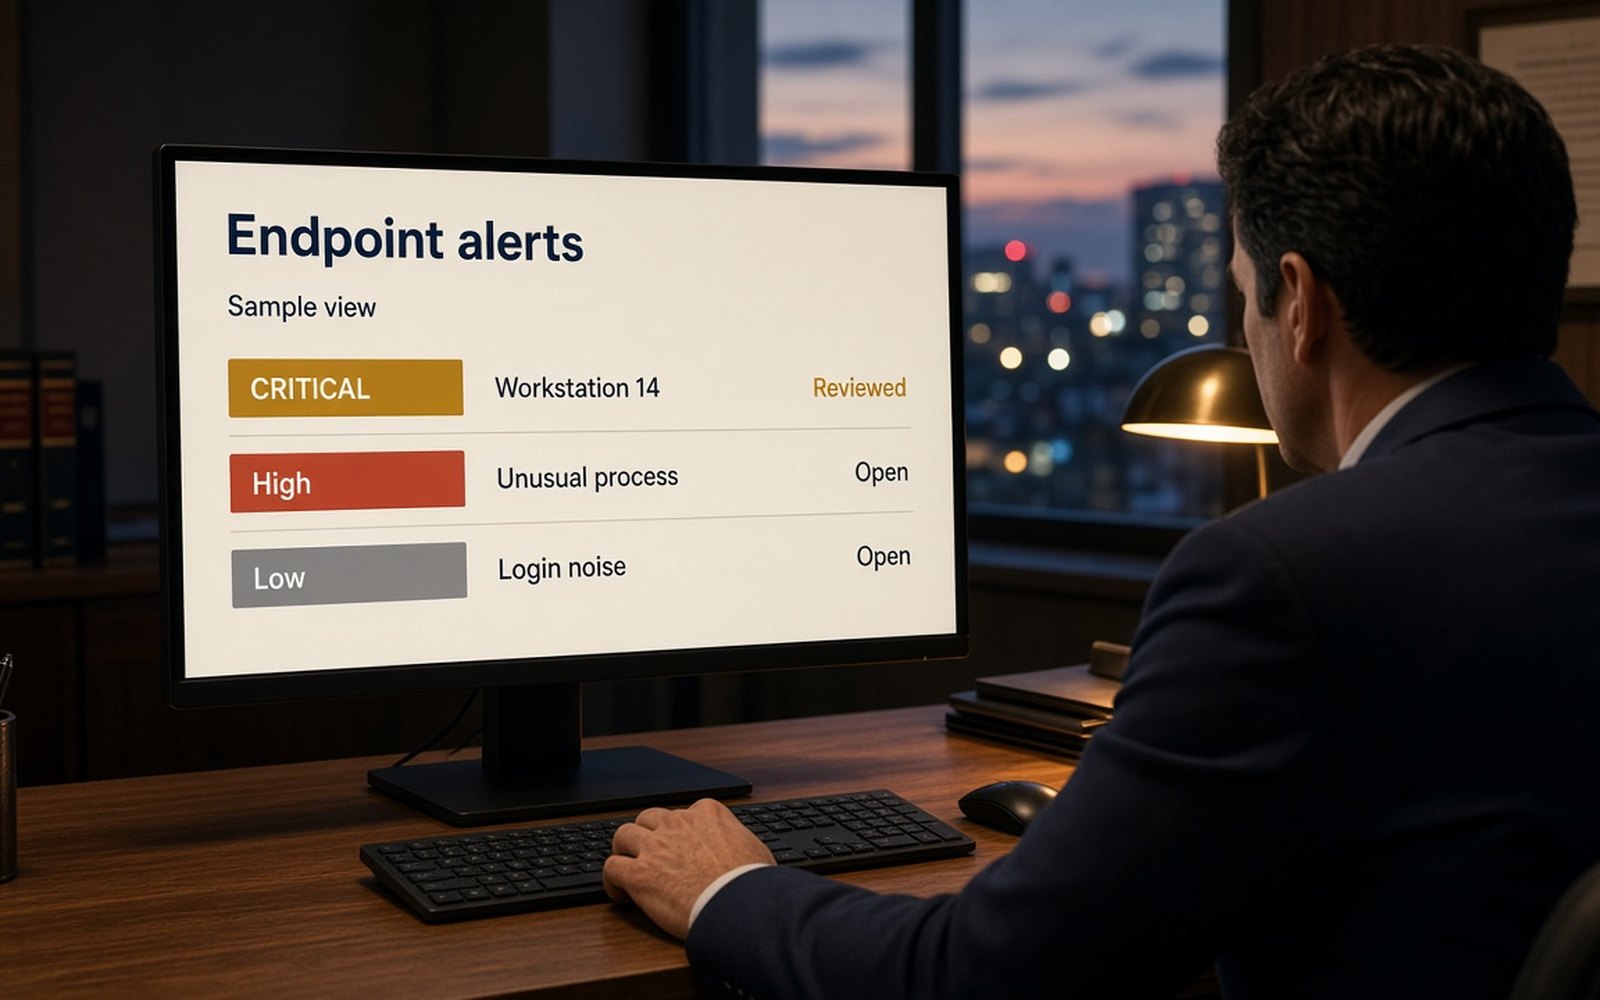
Endpoint and identity tools can raise alerts on every paid plan. A person reviews critical alerts. Isolation is analyst-confirmed, and only when the agreement authorizes it. This page does not promise that a threat cannot spread.
Alert acknowledgment, investigation, containment, remediation, and restoration are different steps. This website does not state a minute-based response promise. Any time commitment is only what a signed agreement says, and it does not mean the incident is remediated or that systems are restored in that time.
Contracted security analysts, when a security operations provider is used, are not described as ArisGate employees.